The bot problem that CAPTCHA can't solve, and proof of human can
reCAPTCHA and proof of human are both described as ways to keep bots out. They are solving different problems.
That sounds like a minor distinction. It is not. The problem reCAPTCHA cannot solve is the one that actually breaks most modern applications at scale, and understanding why requires being precise about what each approach is actually testing.
The question reCAPTCHA asks
reCAPTCHA asks: does this session look like it is being driven by a human?
It answers that question by analyzing behavioral signals, mouse movement patterns, typing rhythm, scroll behavior, time-on-page, and scoring the session against a model of what human interaction looks like. When the score falls below a threshold, a challenge appears. When the session passes the threshold, the request goes through.
This is a probabilistic classification problem. The model says "this session has a 94% probability of being human-driven" or "this session has a 12% probability." There is no certainty. There is a threshold and a decision.
The CAPTCHA alternatives overview puts it plainly: passing a puzzle suggests "probably not a simple bot," while a uniqueness check confirms "one real, unique human." That gap between "probably not a bot" and "confirmed unique human" is where most sophisticated fraud lives.
Why the classification approach has structural limits
The behavioral classification approach has three properties that create an inherent ceiling on what it can guarantee.
It can only distinguish, not verify. reCAPTCHA distinguishes sessions that look human from sessions that look automated. It cannot verify that a human is present. A sufficiently realistic simulation of human behavior passes. A human using an unusual device or input method fails. The test is about appearance, not reality.
AI closes the gap from the generation side. The behavioral signals reCAPTCHA uses to classify sessions are learnable. As AI-generated behavior becomes more sophisticated, the behavioral gap between human and bot narrows. Imperva's 2025 research found that advanced bots bypass reCAPTCHA 83% of the time. The classifier can be retrained, but the generation side can improve faster, because the classifier's weights and thresholds are effectively public through its responses.
It tells you nothing about uniqueness. Even a perfect behavioral classifier that correctly identified every session as human or bot would not tell you whether one human is behind one account or one human is behind 10,000 accounts. A legitimate human can pass reCAPTCHA on 10,000 separate accounts just as easily as on one. The attack that matters in most modern abuse scenarios, Sybil attacks, coordinated account farms, bulk promo abuse, scalper networks, depends on one actor controlling many accounts. reCAPTCHA addresses none of this.
The question proof of human asks
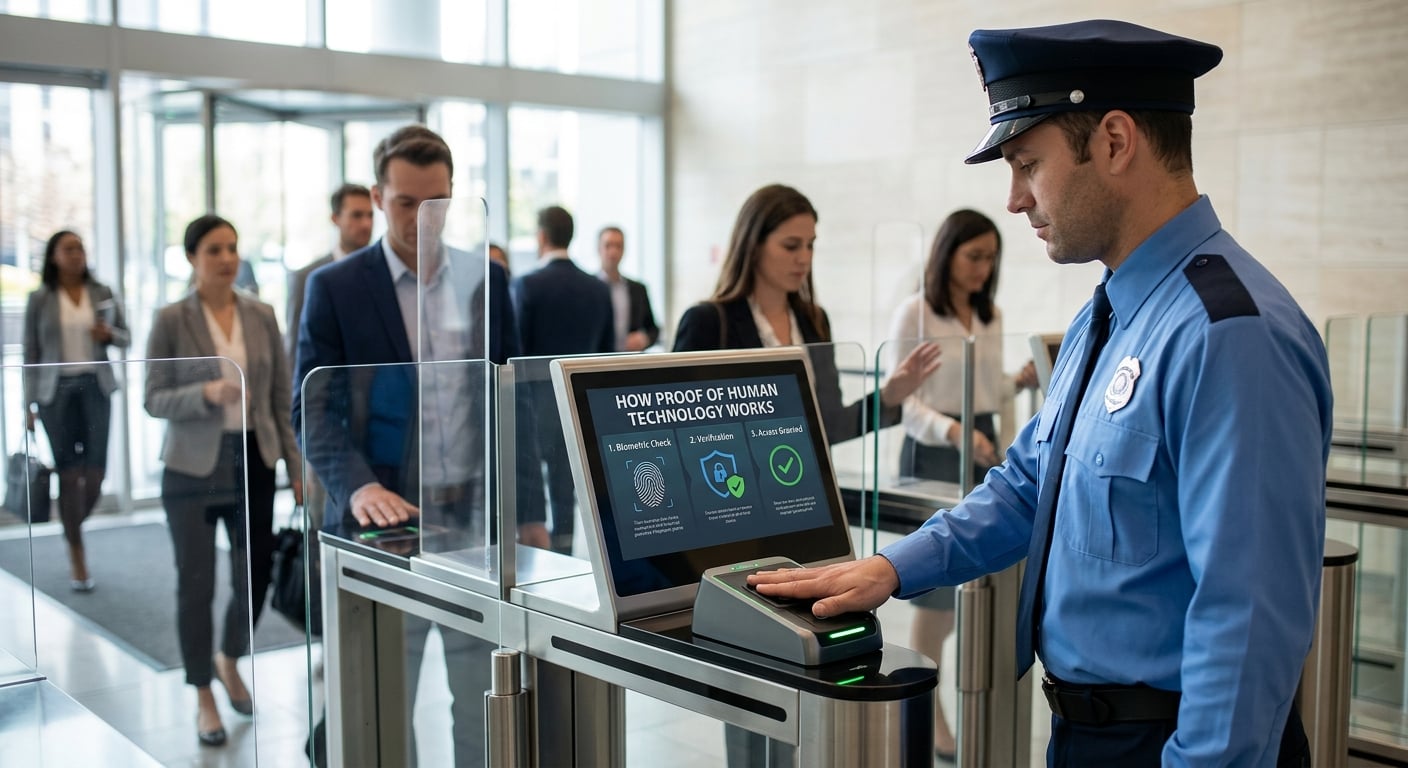
Proof of human asks: is a unique biological human behind this account?
Not "does this session look human." Not "does this request pattern match human timing." Is there a real, specific, unique biological human who has enrolled once and only once in this system?
This is a verification problem, not a classification problem. The answer is not probabilistic. It is a cryptographic confirmation derived from a biometric anchor that cannot be replicated across multiple accounts.
The mechanism: a user completes a one-time enrollment that ties their account to a unique biological identity, generating a cryptographic credential. That credential can be verified by any platform that accepts it. The verification confirms "a unique human is present" without revealing who that human is, zero-knowledge proof handles the privacy requirement.
The proof of human explainer describes the core property: it answers "are you a unique, real person?" rather than "who are you?" The distinction matters because identity is not what most platforms need to confirm, uniqueness is.
What each approach defends against
This is the practical comparison that matters for architects deciding which layer to use where.
reCAPTCHA / behavioral analysis defends against:
Simple automated scripts with no human behavioral simulation
Low-sophistication bots filling forms, posting spam, triggering endpoints at mechanical rates
Scraping that follows obvious non-human patterns
reCAPTCHA does not defend against:
AI-driven bots with realistic behavioral simulation
Coordinated account farms operated by real humans
Sybil attacks where one actor controls many accounts
One human buying 500 limited-edition items across 500 accounts
Promo abuse at scale where the abuser completes each sign-up manually
Proof of human defends against:
Sybil attacks at the account level
One actor controlling many accounts, regardless of how those accounts behave
Bot networks where the bots can convincingly simulate human behavior
Any attack that depends on volume of accounts rather than sophistication of behavior
Proof of human does not defend against:
A malicious verified human acting in bad faith on a single account
Off-platform fraud that happens after the initial account verification
Use cases where the user population cannot complete enrollment
Where each belongs in a production system
The practical answer is not either/or. The two approaches address different attack surfaces and belong in different places.
Behavioral analysis and reCAPTCHA are appropriate when:
The attack is volume-based but account-agnostic, spam forms, endpoint flooding, credential stuffing attempts against existing accounts
The user population cannot or should not be required to enroll in a uniqueness verification system
The cost of a false positive (blocking a real human) is very high and the cost of a false negative (letting a bot through) is low
Proof of human is appropriate when:
The abuse depends on controlling many accounts, ticketing systems, airdrops, limited-supply launches, DAO governance, dating platform integrity
One-person-one-account fairness is a core product property, not a nice-to-have
The user population can reasonably complete a one-time enrollment
A layered defense uses behavioral analysis as the first pass for general bot filtering and proof of human as the gate for actions where uniqueness matters. The two layers are complementary because they are defending against different threat models.
The architecture implication
The key architectural insight is that reCAPTCHA and proof of human operate at different points in the trust model.
reCAPTCHA operates at the session level. Each request is independently scored. There is no persistent state about the human behind the session.
Proof of human operates at the identity level. The credential is persistent across sessions. Once a user has enrolled, every subsequent action they take can carry proof of their uniqueness without re-verification.
For applications where the attack surface is at the account level rather than the session level, session-level defenses are solving the wrong problem. The attacker does not need to fool the session classifier, they need to create many sessions, each of which looks human, because they are being driven by humans in a coordinated farm.
Proof of human moves the defense to the correct layer. The question is not "does this session look human?" It is "can this account prove it was created by a human who has not already created another account?"
That is a different question. It requires a different architecture. And it is the one that actually blocks the attacks that have become routine.
Summary
reCAPTCHA asks "does this session look human?", a probabilistic classification against behavioral signals
Proof of human asks "is a unique human behind this account?", a cryptographic verification against a biometric anchor
reCAPTCHA cannot address Sybil attacks, coordinated account farms or volume-based abuse where each account passes the human behavior test because it is driven by a real human
Proof of human cannot be defeated by realistic bot behavior, because it does not test behavior at all
The two approaches are complementary: behavioral analysis at the session level, proof of human at the identity level
Matching the defense to the threat model is the architectural decision, session-level defenses do not address account-level attacks